#security
5 entries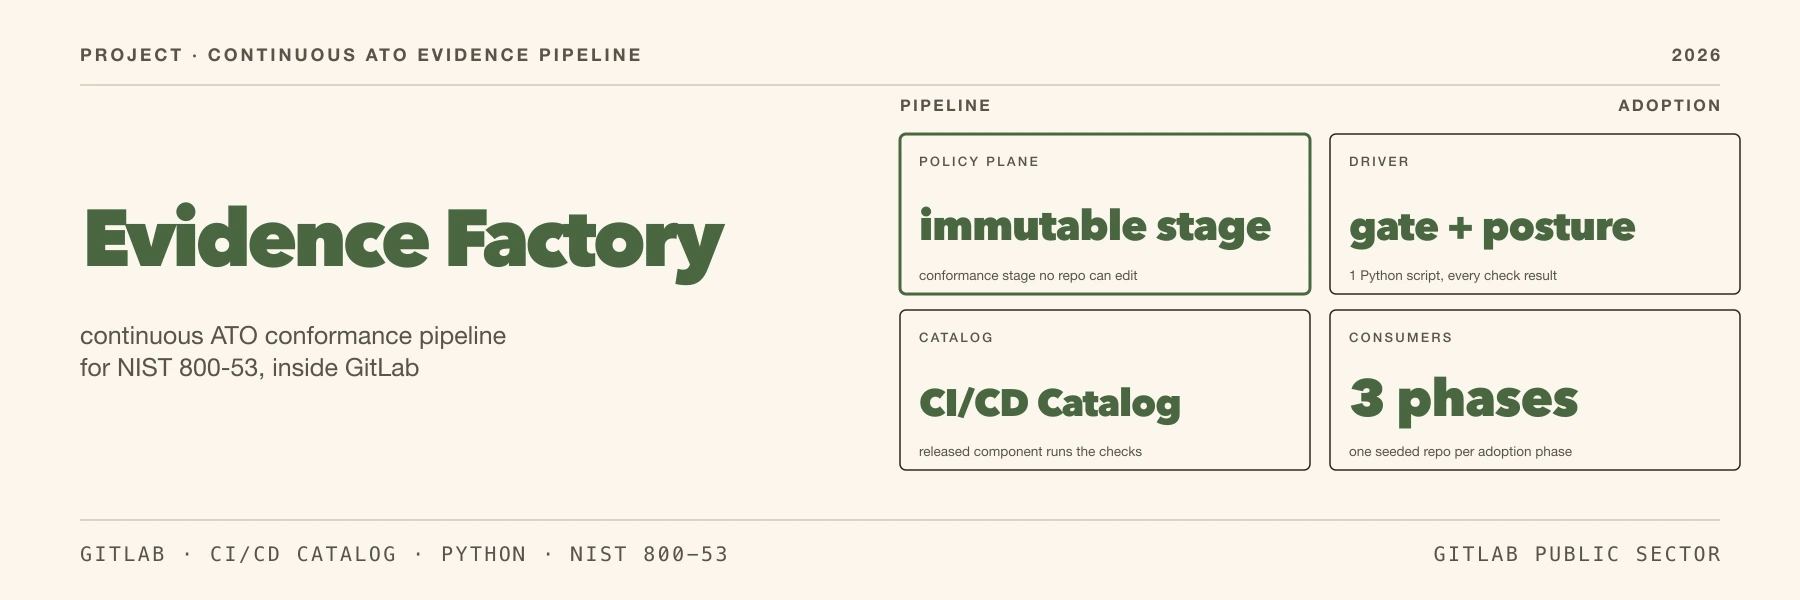
projects · July 2026
Evidence Factory
A worked demonstration of running a continuous ATO evidence pipeline for NIST 800-53 controls entirely inside GitLab: a policy plane injects a conformance stage no repository can edit, a released CI/CD Catalog runs the checks, and one Python driver turns each result into a merge gate and a control posture.
projects · July 2026
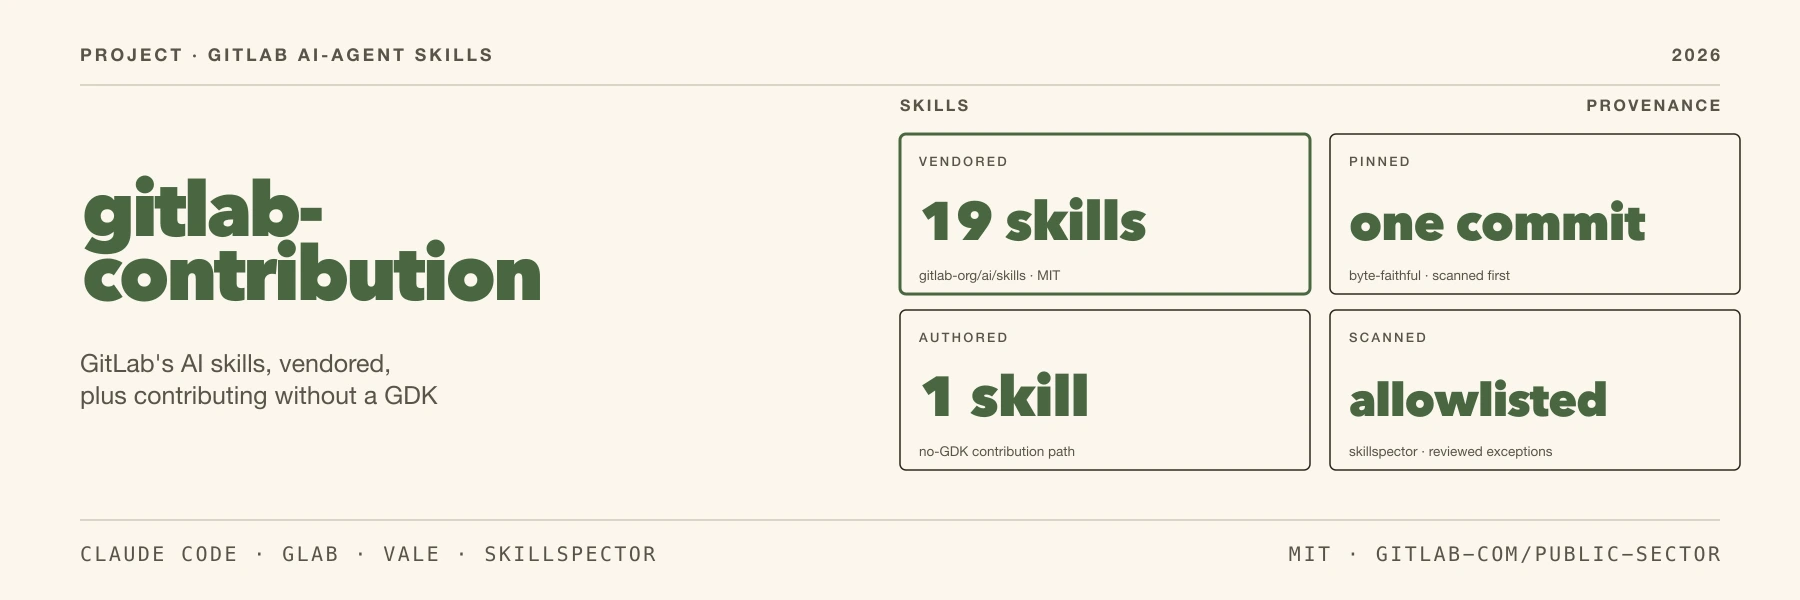
gitlab-contribution
Vendors GitLab's official AI-agent skills for Claude Code at a pinned commit, plus one authored skill for contributing to GitLab projects without a GitLab Development Kit.
writing · July 2026
Service-to-Service Routing in Rootless Podman
Part one isolated the network planes. The sequel: if every service is in its own plane, how do they talk? The answer is FQDN-everywhere through one always-available local router. Getting there meant a hunt through link-local host access, an SSRF guard that rejected it, pasta's --map-guest-addr, and a careful reading of what podman upstream has actually decided. Plus an epilogue: what happened when the pattern met the whole fleet, and the upstream patch that lets the workaround retire.
writing · June 2026
Network Plane Isolation in Rootless Podman
Two podman networks alone don't segment traffic in rootless mode, and isolate=true silently fails when netavark uses its iptables backend (the default on Fedora 43 and earlier) thanks to an iptables-nft bug. The root cause, the fix, and how Fedora 44 made it disappear.
projects · April 2026
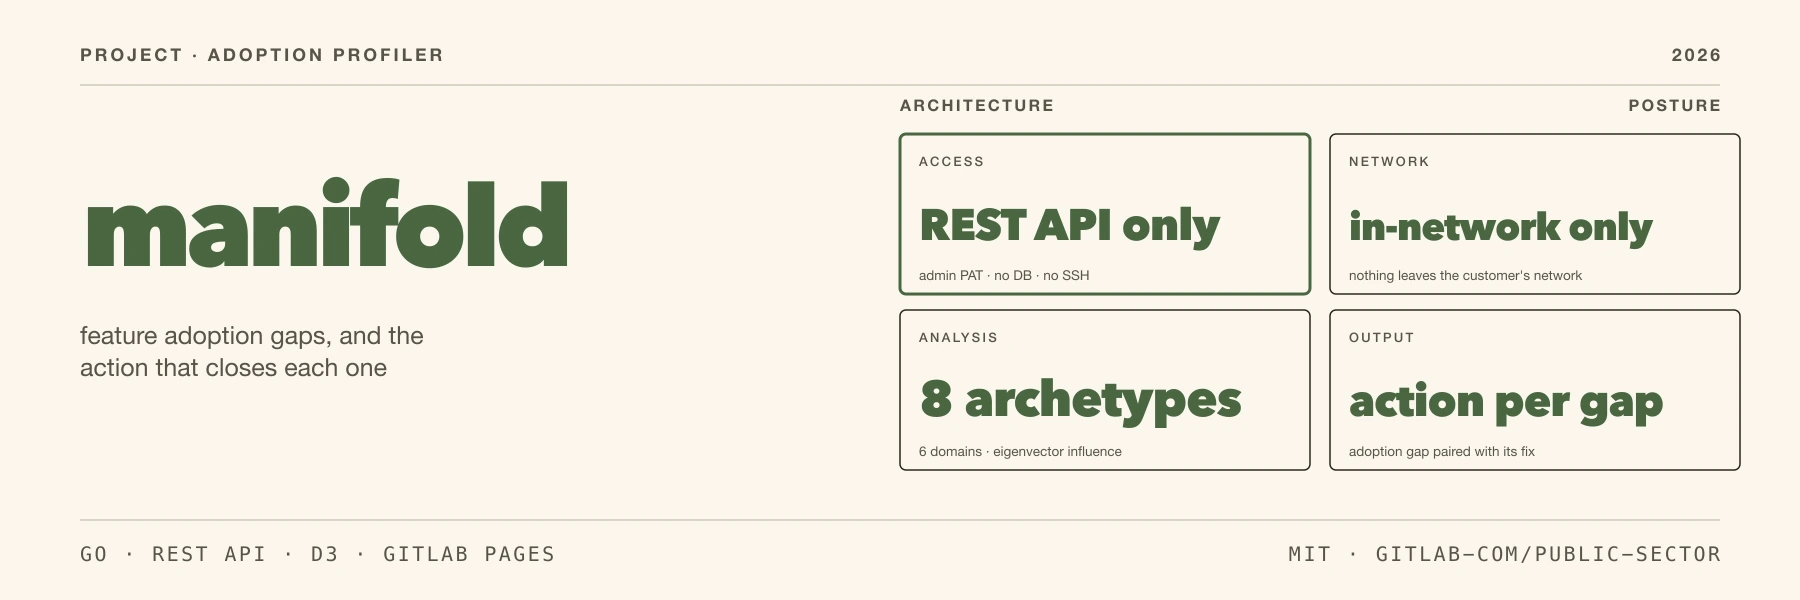
manifold
An API-only adoption profiler for self-managed GitLab: it reads activity through the REST API and renders a dashboard of adoption gaps and the enablement action that closes each one, entirely inside a customer's own network.