#secure-boot
2 entries
writing · September 2026
The Key in the Wrong Keyring
We wanted to sign everything for cairn in CI, including a key for kernel modules, and reached into shim's part of the boot chain without asking first.
projects · July 2026
Cairn
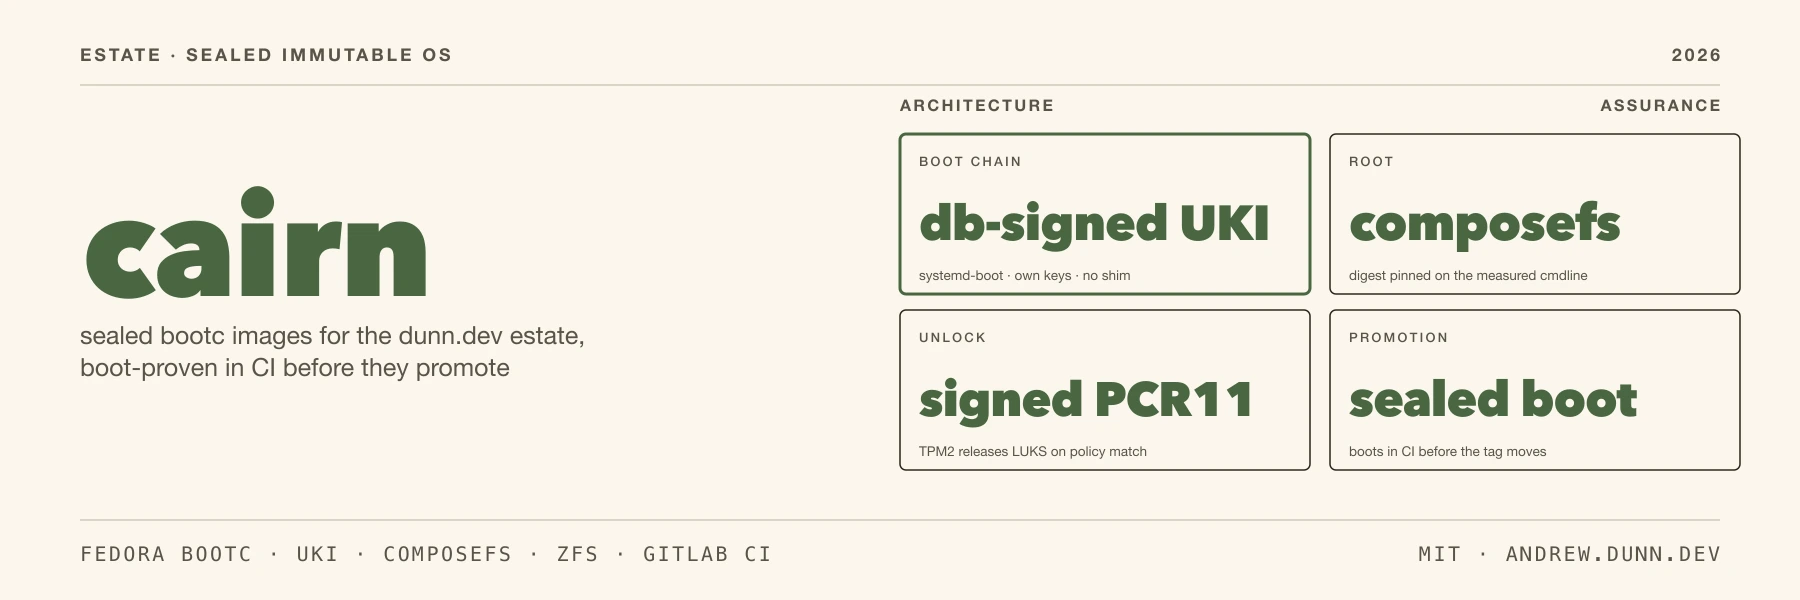
A sealed bootc estate: db-signed UKI boot under keys from an offline ceremony, composefs-pinned root, TPM2 unlock bound to a signed PCR11 policy. Images promote only after booting for real in CI.