#containers
7 entries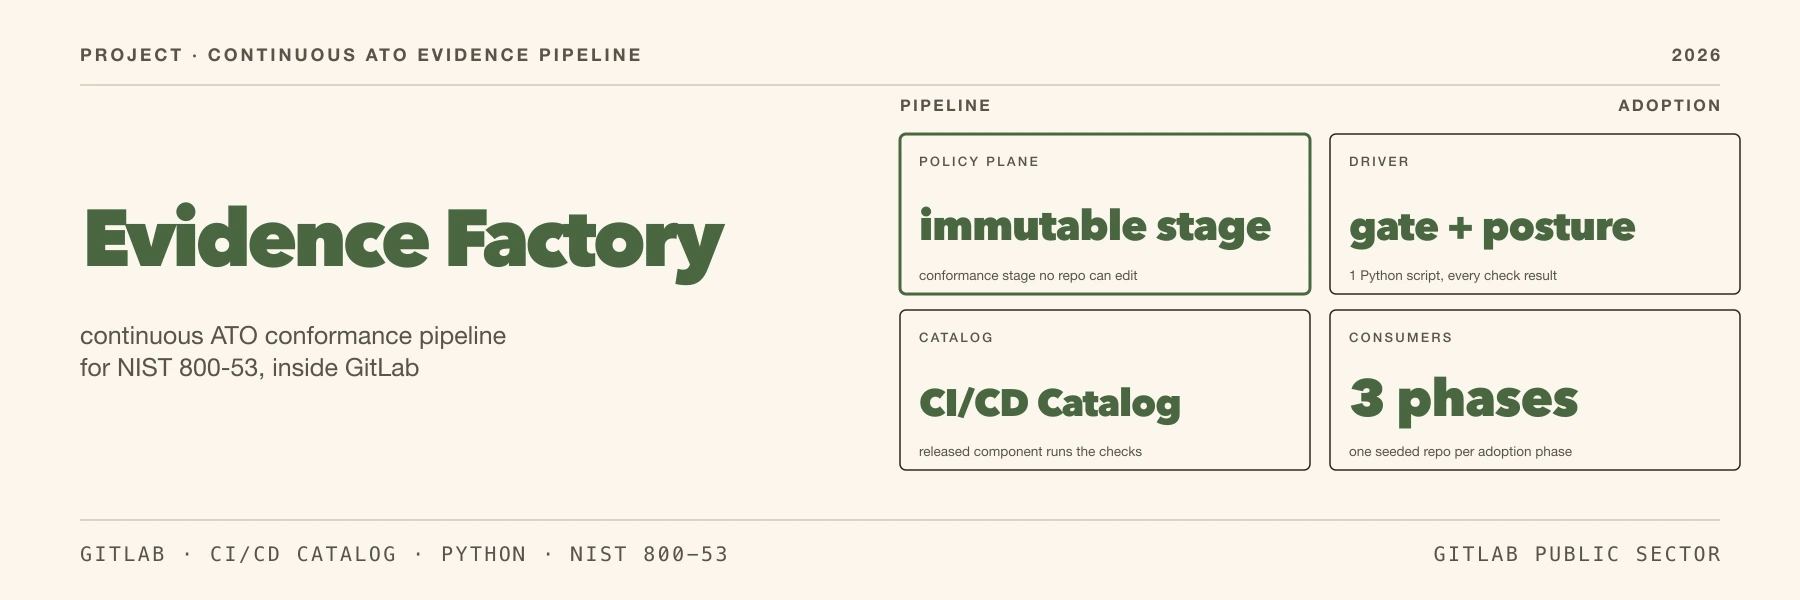
projects · July 2026
Evidence Factory
A worked demonstration of running a continuous ATO evidence pipeline for NIST 800-53 controls entirely inside GitLab: a policy plane injects a conformance stage no repository can edit, a released CI/CD Catalog runs the checks, and one Python driver turns each result into a merge gate and a control posture.
writing · July 2026
Service-to-Service Routing in Rootless Podman
Part one isolated the network planes. The sequel: if every service is in its own plane, how do they talk? The answer is FQDN-everywhere through one always-available local router. Getting there meant a hunt through link-local host access, an SSRF guard that rejected it, pasta's --map-guest-addr, and a careful reading of what podman upstream has actually decided. Plus an epilogue: what happened when the pattern met the whole fleet, and the upstream patch that lets the workaround retire.
projects · July 2026
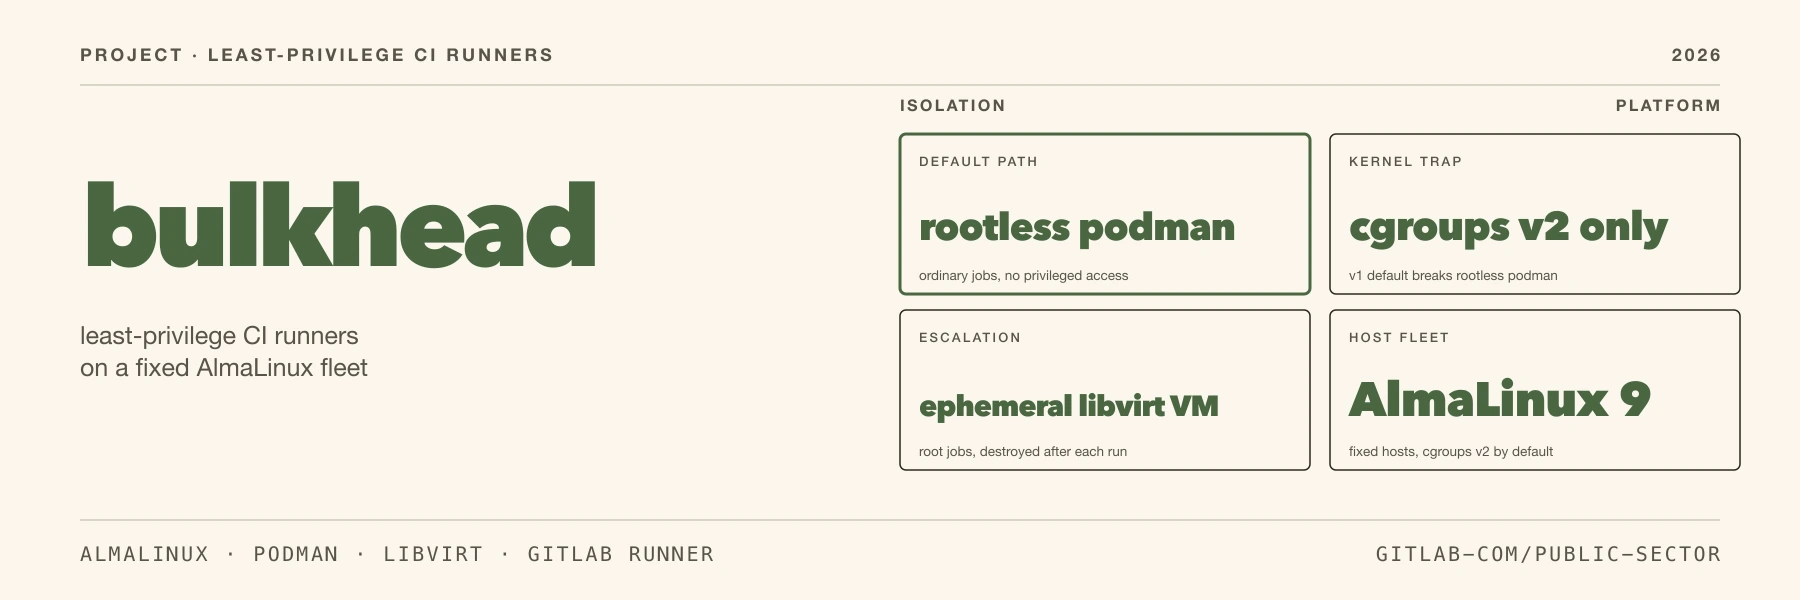
bulkhead
Least-privilege self-managed GitLab CI runners on a fixed set of AlmaLinux hosts: rootless Podman for ordinary jobs, ephemeral libvirt VMs for jobs that need root, and the cgroups v1 versus v2 trap that decides which release to build on.
writing · June 2026
Network Plane Isolation in Rootless Podman
Two podman networks alone don't segment traffic in rootless mode, and isolate=true silently fails when netavark uses its iptables backend (the default on Fedora 43 and earlier) thanks to an iptables-nft bug. The root cause, the fix, and how Fedora 44 made it disappear.
writing · March 2026
Building Bootc Images from Scratch
The upstream Fedora bootc images ship 523 packages. We built one with 255 from scratch using dnf --installroot and a Containerfile. No rpm-ostree, no treefile, no inheritance.
writing · March 2026
Kernel Modules as Multi-Stage Container Builds
A pattern for building ZFS and NVIDIA kernel modules in multi-stage container builds for bootc immutable images. No DKMS, no gcc, no kernel-devel in your production OS.
writing · March 2026
Rootless Podman Pods Leak Subordinate UIDs
Rootless Podman pods leak subordinate UIDs onto the host filesystem. The pod abstraction was the constraint, and named networks fix it completely.